One missed privacy rule can sink a great app.
You spend months building it. Then a user complains. Or a data leak hits the news. Suddenly the Information Regulator wants answers.
Fines of up to R10 million are possible in some cases. Lost trust can cost even more.
The good news? POPIA compliance for app developers is not scary. You just need a clear plan.
This guide covers the data apps collect, the eight conditions, security, breaches, cloud rules, costs, and a launch checklist.
What Is POPIA Compliance for App Developers?
POPIA stands for the Protection of Personal Information Act 4 of 2013. It is South Africa's main data protection law.
The law took full effect on 1 July 2020. Businesses then got one year to catch up. That grace period ended on 30 June 2021.
So what does compliance mean? Your app must handle personal information the way the law says. Collect it fairly. Protect it well. Respect user rights.
POPIA compliance in South Africa matters for mobile apps because apps collect a lot. Names, phone numbers, locations, payments, and sometimes health data.
Three groups need to care. The app owner. The developers. And any vendor that stores or handles the data.
POPIA calls the app owner the responsible party. This is the one who decides why and how data is used.
A developer or cloud host is often an operator. It processes data on the owner's behalf. The person using the app is the data subject.
What about apps built overseas? They can still fall under POPIA. This can happen when they process personal information using means in South Africa.
POPIA also works alongside PAIA, the Promotion of Access to Information Act 2 of 2000. The POPIA Regulations add more practical detail.
What Types of Personal Information Do Mobile Apps Collect?
Most apps collect more than owners realise. Here are the common types.
- Names, email addresses, phone numbers, and identity numbers
- Location data, device identifiers, and usage analytics
- Payment details and other financial information
- Health records, biometric data, and children's information
- Data picked up by third-party SDKs and APIs
Location and device data count as personal information when they can point to a real person. In apps, that is often the case.
Some data needs extra care. POPIA calls it special personal information.
It covers health, biometric information, religious or philosophical beliefs, political opinions, and criminal behaviour.
Children get extra protection too. Under POPIA, a child is anyone under 18.
Section 34 sets a general bar on processing a child's information. Section 35 then lists exceptions.
One exception is prior consent from a parent or guardian. Others include a legal right or duty, and research with safeguards.
So parental consent is not the only route. The right ground depends on your case. Get advice before you collect a child's data.
Identity numbers deserve a special mention. A South African ID number reveals a birth date and gender.
Do not collect it unless you truly need it. Many apps ask for it just in case. That habit is risky.
Here is a common mistake. A team forgets that a third-party SDK sends device IDs to an analytics vendor. Nobody listed it.
The lesson? List every SDK and API before launch. Ask what each one collects and where it sends the data.
The Eight Conditions for Lawful Processing Under POPIA
The eight conditions sit in Chapter 3 of POPIA. Think of them as the backbone of the law.
Use them as a design checklist. Measure every feature against them.
Condition 1: Accountability
Section 8 says the responsible party must make sure all eight conditions are met. That duty does not move to a vendor.
Example. A food delivery startup names one person to own privacy decisions. Developers know who to ask. Nothing falls through the cracks.
Condition 2: Processing limitation
Collect only what you need. Do it lawfully and fairly. Where possible, collect it straight from the user.
Many people think consent is always required. It is not. Section 11 lists other grounds too.
These include a contract, a legal duty, and a legitimate interest.
Example. A fitness app needs an email address to create an account. That fits the contract ground.
Sharing data with an advertiser is different. That needs a proper ground, often consent.
Condition 3: Purpose specification
Section 13 says you collect data for a specific and lawful purpose. Tell people what that purpose is.
Section 14 says do not keep records longer than needed. Then delete them or strip out the details that identify a person.
Example. A taxi app uses location to match riders and drivers. It should not keep old trip history forever.
Set a retention schedule. Then stick to it.
Condition 4: Further processing limitation
A new use must fit the original purpose. If it does not, you need a new lawful basis.
Example. A diet app collects health data for meal plans. Using it to sell insurance leads is a big no.
Condition 5: Information quality
Keep data complete, accurate, and up to date. Bad data hurts users.
Example. A user mistypes their ID number at sign-up. Let them fix it on the profile screen. Simple, and it protects both sides.
Condition 6: Openness
Sections 17 and 18 cover this. Keep records of your processing. Tell users what you collect, why, and who gets it.
Example. Show a short collection notice at sign-up. Name the app owner. State the purpose. Explain user rights and any transfers abroad.
Condition 7: Security safeguards
Sections 19 to 22 cover security. You must use appropriate and reasonable technical and organisational measures.
Operators must follow the same standard. They also need a written contract with you.
Example. Encrypt data, limit admin access, and log security events. I cover this in detail below.
Condition 8: Data subject participation
Sections 23 to 25 let users ask what you hold. They can also ask you to correct or delete it.
Example. Add a "Request my data" button in the settings menu. It saves your support team hours.
One more point. Consent is only one lawful ground. Do not build every feature around a pop-up.
Key POPIA Requirements for Mobile Apps Every Developer Must Follow
Let us turn the law into a to-do list. These are the duties teams miss most.
The POPIA requirements for mobile apps are easier to meet when you plan them early. Work with a custom software development company to build these rules into the design from day one. Fixing them later costs more.
Collect only what the app needs
Ask this for every field. Do we truly need it?
A weather app does not need an ID number. Less data means less risk.
Pick a lawful basis
Choose the right ground under Section 11 for each purpose. Write it down. Different features may use different grounds.
Get consent when it is required
When you rely on consent, make it voluntary, specific, and informed. No pre-ticked boxes.
Keep consent records. Store the date, the version of the notice, and what the user agreed to.
Write a clear privacy policy and collection notice
Section 18 asks for a notice when you collect data. Cover what you collect, why, who receives it, and how to reach you.
Include the Information Regulator's details and the right to complain.
A privacy policy alone is not enough. The policy only matters if the app matches it.
Some apps have beautiful policies and sloppy practices. Do not be that team.
Let users access and correct their information
Build simple screens for these requests. Set a clear way to verify the user's identity first. That blocks fraud.
Set retention and deletion rules
Decide how long you keep each data type. Then build deletion into the system. Do not rely on someone remembering.
Protect data shared with third-party providers
Sign written agreements with every operator. Check what they do with your data. Ask where they store it.
Quick view of the main duties
This table helps your team scan the key points.
| POPIA requirement | What the app team should do | Section of the Act |
|---|---|---|
| Lawful processing | Pick and record a lawful ground for each purpose | Section 11 |
| Specific purpose | Define the purpose and set a retention schedule | Sections 13 and 14 |
| Notice to users | Show a clear collection notice at sign-up | Section 18 |
| Security | Use reasonable technical and organisational measures | Sections 19 to 22 |
| User rights | Build access, correction, and deletion tools | Sections 23 to 25 |
| Direct marketing | Get consent or use the customer exception, with opt-out | Section 69 |
| Cross-border transfers | Meet one of the transfer conditions | Section 72 |
How to Build a POPIA-Compliant Mobile App Step by Step
Here is a practical way to approach POPIA compliance for app developers on real projects. The order matters.
Follow it from the first sprint. Not the last week.
Step 1. Map the personal information your app collects
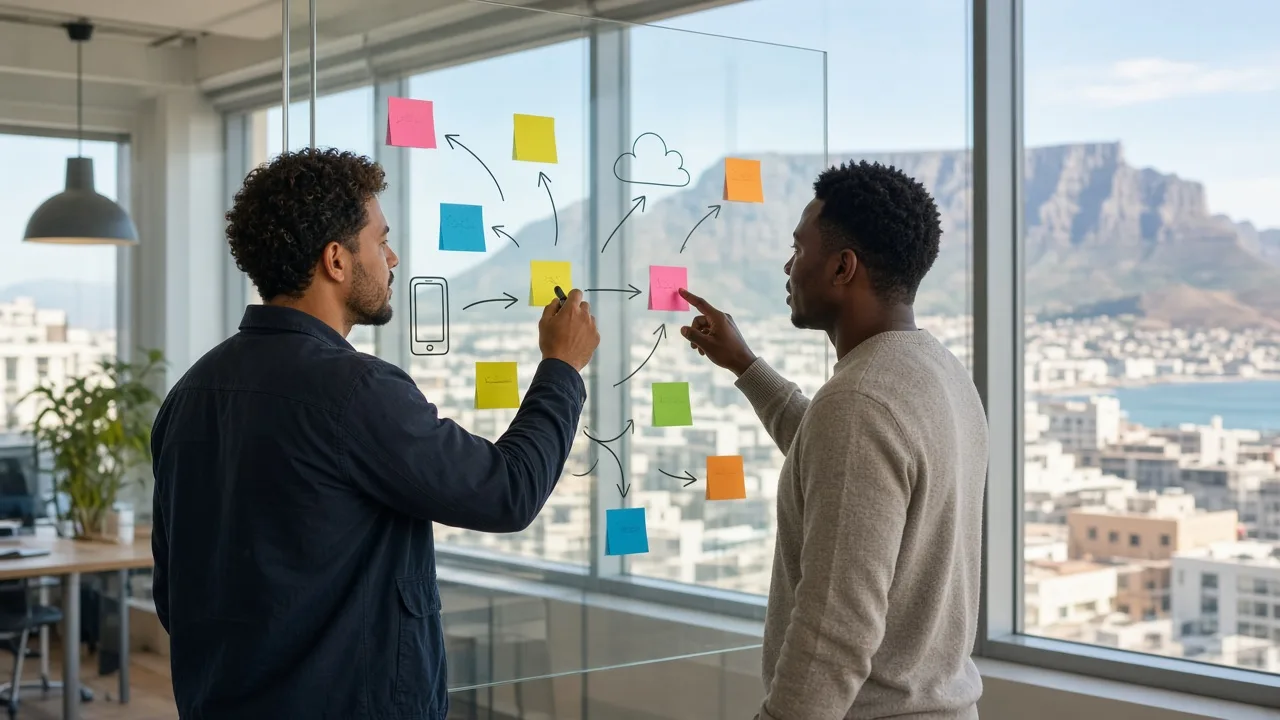
Create a data inventory. List every field, where it comes from, where it goes, and who can see it. Draw a simple data flow map.
Example. A delivery app collects name, phone, address, and live location.
The map shows the address also goes to a maps API and an SMS provider. Good catch.
Step 2. Identify your role as a responsible party or operator
If you decide why and how data is used, you are the responsible party. If you only process data for a client, you are an operator.
Real life gets blurry. Say you build an app for a client. You are often the operator.
But if you add your own analytics for your own goals, you may become a responsible party for that data.
Step 3. Conduct a personal information impact assessment
Ask what could go wrong for users. Rate each risk. Decide how to reduce it.
Some people call this a privacy impact assessment. The POPIA Regulations put this task on the Information Officer's list.
Step 4. Design privacy notices and consent flows
Keep notices short and layered. Show the key points first. Link to the full policy.
Ask for permission at the moment of need. Save a consent record every time. Add a preference management screen so users can change their choices.
Step 5. Secure databases, APIs, and user accounts
Use multi-factor authentication for admins. Apply role-based access control and least privilege. Each person sees only what the job needs.
Protect sessions with short timeouts. Secure every API with authentication and access tokens.
Encrypt data at rest and in transit. Manage encryption keys apart from the data. Mask sensitive fields in logs.
Picture a test database that holds real customer data behind a weak password. That is how leaks start.
Step 6. Review third-party SDKs, cloud services, and payment gateways
Do a vendor risk check on each one. Ask what data it collects. Ask where it stores it. Ask how it reports a breach.
Let payment gateways handle card details. Your app should not store full card numbers. That is a smart habit, though POPIA does not name it.
Step 7. Test user data access, correction, and deletion processes
Do not assume these features work. Test them like any other feature.
Create a test user. Request their data. Correct a field. Delete the account. Then check the database, backups, and vendor tools.
Deleted should mean deleted everywhere you control.
Step 8. Document compliance and review it regularly
Keep processing records, your retention schedule, and operator agreements in one place.
Review them every quarter. Review them again before each major release. Apps change fast. Paperwork must keep up.
POPIA Rules for App Permissions, Cookies, Analytics, and Marketing
Permissions are where users decide if they trust you. Handle them with care.
Location, camera, microphone, and contact permissions
Ask only when a feature needs it. Ask at that moment, not at launch. Explain the reason in plain words.
Example. A ride app asks for location when the user taps "Book a ride". A flashlight app asking for contacts is a red flag.
If a user says no, the app should still work as far as possible. Do not punish them.
Push notifications, email marketing, and SMS campaigns
Section 69 covers electronic direct marketing. In general, you need the person's consent first.
There is one exception. You may market similar products to existing customers.
But you must have offered an easy opt-out when you collected their details. You must repeat that offer in every message.
If a person said no once, you may ask for consent only one time. After that, stop.
Every message must say who sent it. It must also show how to opt out.
Advertising IDs, tracking tools, and analytics platforms
POPIA has no special cookie rule. The general conditions still apply.
So tell users about tracking. Have a lawful ground for it.
Use data minimisation in analytics. Remove or hide user IDs where you can. Pseudonymisation helps here.
Also check what each analytics vendor keeps and for how long.
Consent withdrawal and marketing opt-outs
Users must be able to withdraw consent as easily as they gave it. One tap in settings is ideal.
Honour it fast. Sync it across email, SMS, and push tools.
Here is a common slip. Unsubscribe works on email only. SMS keeps flowing. Complaints follow. Check every channel.
Data Security and Breach Reporting Requirements Under POPIA
Security is where good intentions meet real attackers. This part deserves your best work.
POPIA asks for appropriate and reasonable measures. It does not name tools. So encryption and similar controls are recommended practices that support your duty.
They do not prove compliance on their own. Keep that difference clear. Strong mobile app data protection is a habit, not a single tool.
Encryption, authentication, access controls, and secure APIs
Use encryption in transit and at rest. Use strong sign-in with multi-factor authentication. Limit access by role.
Lock down every API endpoint. Rotate access tokens. Log security events so you can spot odd behaviour.
Preventing unauthorised access, data leaks, and data loss
Test your app before attackers do. Good software testing in South Africa should include a vulnerability assessment and penetration testing.
Add dependency scanning to catch risky libraries. Add secure code review for sensitive features.
Back up data too. Loss is a security problem as well. Protect the backups with the same care.
What to do after a personal information breach
Sections 21 and 22 cover this. The duties differ for operators and responsible parties.
An operator must tell the responsible party immediately. This applies when it has reasonable grounds to believe a compromise happened.
The responsible party then leads the response. Here are the steps.
- Contain the problem. Cut off access and fix the hole.
- Log the incident and run a breach assessment.
- As the responsible party, notify the Information Regulator as soon as reasonably possible after discovery.
- Notify affected users as soon as reasonably possible too.
- Learn from it and update your incident response plan.
Some limits apply. A public body that handles law enforcement may ask you to delay notice. You may also need time to find the scope and restore system integrity.
Write your incident response plan before you need it. At 2 AM, nobody thinks clearly.
When and how to notify the Information Regulator and affected users
The law says notify as soon as reasonably possible. It does not give a set number of hours.
Tell users clearly. Explain what happened, what data was involved, and what they should do.
The Information Regulator's POPIA guidance explains security compromise notifications and other duties. Bookmark it.
POPIA Requirements for Cloud Storage and Cross-Border Data Transfers
Most apps use cloud hosting. Many servers sit outside South Africa. So this question comes up often.
Does POPIA allow personal information to be stored outside South Africa? Yes, under conditions.
Using international cloud hosting providers
POPIA does not ban foreign hosting. Section 72 sets the rules for transfers.
A transfer must meet at least one specific condition. Here are the main ones.
- The receiver is bound by law, binding corporate rules, or a binding agreement that gives similar protection
- The user consents to the transfer
- The transfer is needed for a contract with the user
- The transfer benefits the user, and getting consent is not practical
Sharing personal information with overseas vendors
Look past the main server. Check backups, support teams, email tools, and analytics vendors. Data often travels further than you think.
Keep a list of countries where data goes. Keep it with your data inventory. That also helps your collection notice.
Understanding Section 72 and applicable transfer safeguards
Section 72 and prior authorisation are two different things.
Prior authorisation comes from Section 57. It applies to certain processing activities only. It does not apply to every international transfer.
One example is sending special personal information or children's information to a country without adequate protection.
Check your case with a privacy professional. Do not guess.
Reviewing contracts with operators and other service providers
Operators must process data only with your knowledge and approval. You need a written operator agreement.
It should cover security, breach reporting, subcontractors, deletion, and where data is stored. Read the standard cloud terms. Do not just click accept.
Information Officer Registration and POPIA Documentation
Paper may feel boring. But in an investigation, your documents speak for you.
The role of the Information Officer
Every business has an Information Officer. For a private company, that is usually the head, like the CEO.
You can appoint Deputy Information Officers to help. The role covers encouraging compliance, handling user requests, and working with the Regulator.
Registering the Information Officer with the Regulator
The responsible party must register its Information Officer with the Regulator. It must do this before the officer starts their duties.
Use the Regulator's eServices portal to register.
Many businesses skip this step. Do not be one of them.
Maintaining privacy policies, processing records, and agreements
Keep a short set of core documents.
- Privacy policy and collection notice
- Processing records and data inventory
- Retention schedule
- Operator agreements
- Breach log and incident response plan
- A PAIA manual, where your business needs one
POPIA Compliance for Different Types of Mobile Apps
Each app type carries its own risks. Here are the ones that show up most in South Africa.
Ecommerce and online payment apps
These apps hold names, delivery addresses, phone numbers, and order history.
Use a trusted payment gateway. Never store card details yourself. Keep order data only as long as you need it.
Healthcare and fitness apps
Health data is special personal information. The bar is higher.
Get clear consent or rely on a specific exception in the law. Limit who can see records. Encrypt everything.
Fintech and digital banking apps
These apps hold IDs, bank details, and transaction history. A leak here is serious.
Large projects like these often need enterprise software development in South Africa with strict access control and audit logs.
Other laws may apply too, such as FICA. POPIA is only one piece.
Food delivery and on-demand service apps
Think about addresses, phone numbers, and live location. Remember driver and courier data too. They are data subjects as well.
Hide customer phone numbers from drivers where you can. Use masked calling.
Education and children's apps
Section 34 sets a general bar on processing a child's information. Section 35 lists the exceptions.
Parent or guardian consent is one route. Others may apply, depending on the case. Get advice on the right grounds.
Collect the bare minimum. Skip ad tracking in children's apps. It is not worth the risk.
AI-powered apps and personalised recommendation systems
Personalisation uses profiling. That can affect people.
Section 71 limits decisions made only by automated means when they have legal or serious effects. Be careful with this in lending or hiring apps.
Apply data minimisation to model data handling. Check any third-party AI service. Ask what it keeps and whether it trains on your users' data.
What Happens If Your App Does Not Comply With POPIA?
Let me be honest. Most companies do not get hit on day one. But the risk is real.
Complaints, investigations, and enforcement notices
Anyone can lodge a complaint with the Information Regulator. The Regulator can investigate. It can then issue an enforcement notice.
Administrative fines and potential criminal liability
POPIA provides for administrative fines of up to R10 million in applicable cases. The amount depends on the facts.
Some offences can also carry imprisonment. The most serious ones can carry up to 10 years.
Users can also claim damages in court. That adds to the bill.
Reputational damage and loss of customer trust
A breach story travels fast. Users delete apps in minutes. Winning them back takes years.
I think trust is the real penalty. Fines end. Doubt lingers.
Practical steps to reduce compliance risks
- Appoint and register your Information Officer
- Map your data and cut what you do not need
- Sign operator agreements
- Test security and your breach plan
- Train your staff
How an App Development Company Can Help With POPIA Compliance
A good development partner cannot replace your lawyer. But it can save you many headaches.
Privacy by design app development
Privacy by design app development means privacy is part of the build, not an add-on. The default settings protect the user.
Secure architecture and data protection controls
Your partner can design secure databases, API security, and access controls. It can also link many tools safely in larger systems.
Compliance documentation and testing
They can help with data maps, processing records, and test plans. They can also test deletion and correction flows.
Working with legal and data protection specialists
The best results come from teamwork. Developers build. Lawyers check the legal side. Your Information Officer ties it together.
Conclusion: Make POPIA Compliance Part of Your App Strategy
POPIA compliance for app developers starts with knowing what data your app collects and why.
From lawful processing and user consent to secure APIs, operator agreements, and breach reporting, every step matters. South African businesses should build privacy into development from day one, not patch it in after a problem.
Review your data flows, check third-party SDKs, and give users clear ways to access or correct their information.
A secure app protects more than data. It builds trust that keeps users coming back.
FAQs About POPIA Compliance for App Developers
What is POPIA compliance for app developers?
It means collecting, using, storing, and sharing personal information in line with South Africa's data protection law.
Does every mobile app in South Africa need to comply with POPIA?
If an app processes personal information in a way covered by POPIA, its responsible party must meet the law's requirements.
Is user consent always required under POPIA?
No. Section 11 lists other lawful grounds, including contracts, legal duties, and legitimate interests. The right ground depends on the purpose.
What are the eight conditions for POPIA compliance?
They cover accountability, processing limitation, purpose specification, further processing, information quality, openness, security safeguards, and data subject participation.
How should app developers protect personal information under POPIA?
Use suitable security controls, limit access, encrypt data, review third-party tools, and keep written operator agreements in place.
What should a business do after a data breach under POPIA?
The operator must notify the responsible party immediately. The responsible party must notify the Regulator and affected people as soon as reasonably possible.
Can South African apps store personal information overseas?
Yes. Section 72 allows cross-border transfers when at least one of its legal conditions is met.
What are the penalties for POPIA non-compliance?
Applicable cases can carry administrative fines of up to R10 million. Certain offences may also lead to imprisonment or civil claims.